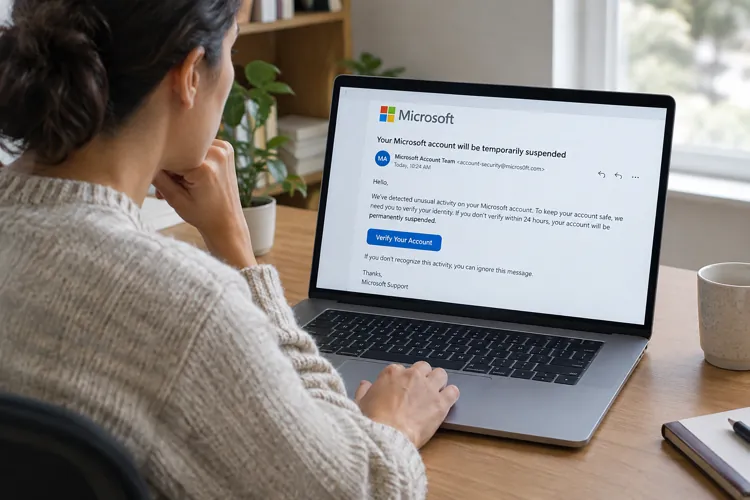
A phishing email posing as a Microsoft 365 notification tells recipients to verify their accounts or risk deactivation.
Warning signs include an unrelated sender address, a misspelled sender name and a verification link that leads away from Microsoft.
Recipients should report the message as phishing and check their accounts through their usual Microsoft apps or bookmarks.
An email claiming Microsoft is deactivating inactive accounts illustrates how scammers use familiar branding, threats and personalized information to lure recipients into clicking suspicious links. It may not be a coincidence that the email is hitting in-boxes in the hours after Microsoft’s outage.
The message displays “MICROSOFT 365” above a brief warning: “We are deactivating all Inactive Microsoft accounts.” It then identifies the recipient’s email address and asks them to confirm that the account remains active by clicking a “Verify Now” button.
According to a ChatGPT analysis, the message contains several strong signs of phishing, a scheme designed to trick people into revealing passwords or other sensitive information. Microsoft identifies urgent demands, unfamiliar sender addresses and suspicious links as common warning signs.
The sender doesn’t match the claim
One of the clearest clues appears in the sender information. Although the email claims to concern Microsoft 365, the displayed sender address uses a well-drilling company’s domain.
That mismatch should prompt immediate skepticism. A Microsoft label in the body of an email does not authenticate its source.
The sender’s display name also contains an error: “System.Notifcation,” with “Notification” misspelled. A string of numbers follows the name, while a lengthy “ACTION ID” adds an appearance of technical authority.
Neither identifier establishes that the message is legitimate.
A familiar address hides an unfamiliar destination
The “Verify Now” link provides another major warning.
Its address begins with a Google domain, but the link contains a redirect to an unrelated website using a Nigerian country-code domain. The destination is not a Microsoft sign-in address.
The concern is the mismatch between the claimed service and the destination—not the country associated with the website. A familiar name at the beginning of a long link does not establish that the final destination is trustworthy.
The destination’s path also includes WordPress-related directories and seemingly random characters. Those details do not independently prove fraud, but they provide no credible connection to Microsoft account verification.
Personalization doesn’t prove authenticity
The message includes the recipient’s actual email address, which may make the warning seem more convincing.
The same address also appears in encoded form within the link. That could allow the destination page to prefill an email field or tailor the page to the recipient. However, possessing someone’s email address does not demonstrate access to that person’s account.
The generic greeting, “Attention Members,” and awkward wording add to the warning signs. The threat of deactivation supplies pressure to act before examining those details.
How recipients should respond
Anyone receiving this message should report it as phishing through their email service and delete it. To investigate a possible account issue, open the Microsoft app directly or use a trusted bookmark. Microsoft recommends visiting a company’s official website independently instead of following links in a suspicious message.
Anyone who entered a password after following the link should change it through the official service immediately, notify their organization’s email administrator and enable multifactor authentication. Microsoft also recommends contacting workplace IT support when a suspected phishing incident involves a work account.